CFW provides a cluster-mode VPC Firewall to protect inter-VPC traffic within a Cloud Connect Network (CCN). The cluster mode adopts a fully managed architecture, where Tencent Cloud maintains firewall clusters in all regions, eliminating the need for users to deploy and maintain instances themselves.
On the VPC Firewall (Cluster) page, the system automatically detects CCN instances under the current account, and you can configure the corresponding Firewall Toggle for them.
Access Impact
When the VPC Firewall is connected to, a network jitter of 1-2 seconds occurs at the moment the route takes effect, as route rules need to be dynamically published to achieve traffic steering. During this period, traffic between CVMs across VPCs or within the same VPC is not interrupted and is only perceived as brief latency fluctuations.
Note:
This network jitter is a normal technical phenomenon during route publishing. It is recommended to perform the Firewall Toggle enabling operation during off-peak business hours and verify the automatic reconnection capability of critical services in advance.
Firewall Toggle
1. Log in to the CFW console, and in the left sidebar, choose Firewall Toggle > VPC Firewall (Cluster).
2. On the VPC Firewall (Cluster) page, locate the CCN instance that needs protection in the Protection Object column, and enable the Firewall Toggle.
Note:
Enabling protection for each CCN instance consumes one general instance quota. Ensure that you have sufficient quota before enabling it.
3. In the pop-up window, select the access mode:
Automatic Access: CFW automatically coordinates with CCN to configure the policy-based routing table based on the configured VPC traffic steering policy.
Note:
The automatic access mode relies on the policy-based routing feature of CCN. This feature is currently in public beta and is unavailable by default. To try this feature, submit a ticket to CFW.
Manual Access: In manual access mode, you need to manually configure traffic diversion in the CCN console.
5. In the instance list, you can disable or edit CCN instances that have protection enabled.
Note:
After the Firewall Toggle is disabled, relevant network assets (such as VPCs and subnets) used by the current CCN-type instance to access the firewall will be automatically cleared.
If the access mode of the current protection object is Manual Access, you must manually cancel the access of this CCN instance in the CFW console before disabling the Firewall Toggle. Otherwise, directly disabling the toggle may cause network interruption. For detailed steps, see Disconnecting a CCN Instance from CFW (Multi-Route Table).
If intra-city direct connection (intra-city traffic diversion) between intra-region VPCs has been enabled for this CCN instance, the rollback process may affect existing business connections, causing session interruptions or even network disconnection. For details, see VPC Firewall.
Spec Adjustment
On the VPC Firewall (Cluster) page, click Expand to redirect to the purchase page, where you can expand parameters such as bandwidth and log storage capacity.
In cluster mode, all CCN instances with the toggle enabled share the VPC firewall bandwidth, so you don't need to adjust settings for individual instances.
Starting from June 10, 2026, the business traffic overflow control mechanism will be officially enabled in cluster mode. For details, see Will business be affected if the business bandwidth exceeds the VPC Firewall bandwidth limit? in FAQs - Bandwidth.
Protection configuration
1. Log in to the CFW console, select Firewall Toggle in the left sidebar, and click Firewall Settings in the upper-right corner.
2. In the Protection Configuration area, you can configure protection settings for the VPC Firewall:
TCP blocking action: When the firewall blocks a TCP session, define the blocking method.
Packet Loss Only: directly drops packets (the client perceives this as a connection timeout).
Drop Packets and Reset Connection: drops packets and sends an RST packet to the access source (the client immediately receives a connection refused signal).
Synchronizing Assets
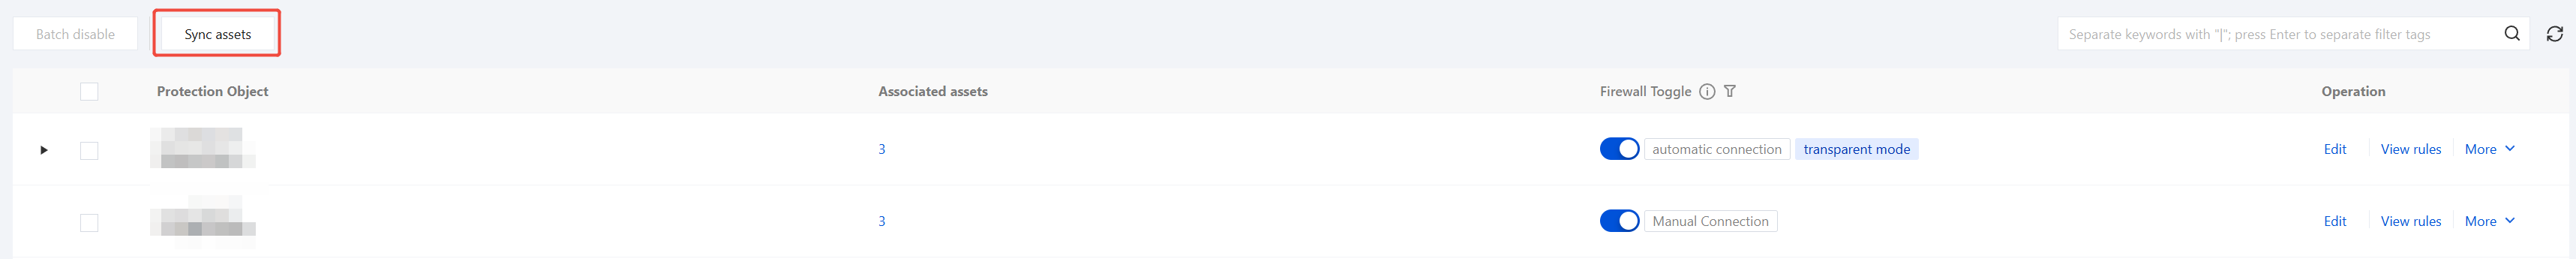
The backend polls user asset information at a fixed interval of 5 minutes. If asset changes occur within this interval but have not yet been synced by the backend, click Sync assets above the list to promptly call the backend API to re-read and sync asset information and data.
If newly added assets do not appear in the Firewall Toggle list, you can click Sync assets above the list to attempt synchronization.
Transparent Mode
On the VPC Firewall (Cluster) page, click More and select Enable Transparent Mode from the drop-down list. In transparent mode, the current firewall instance only forwards network traffic, and the access control and intrusion defense features do not take effect. It is recommended for debugging purposes and is expected to take effect within 1 minute after being enabled. After debugging, manually disable transparent mode. If you need more help, submit a ticket.
Firewall Status Monitoring
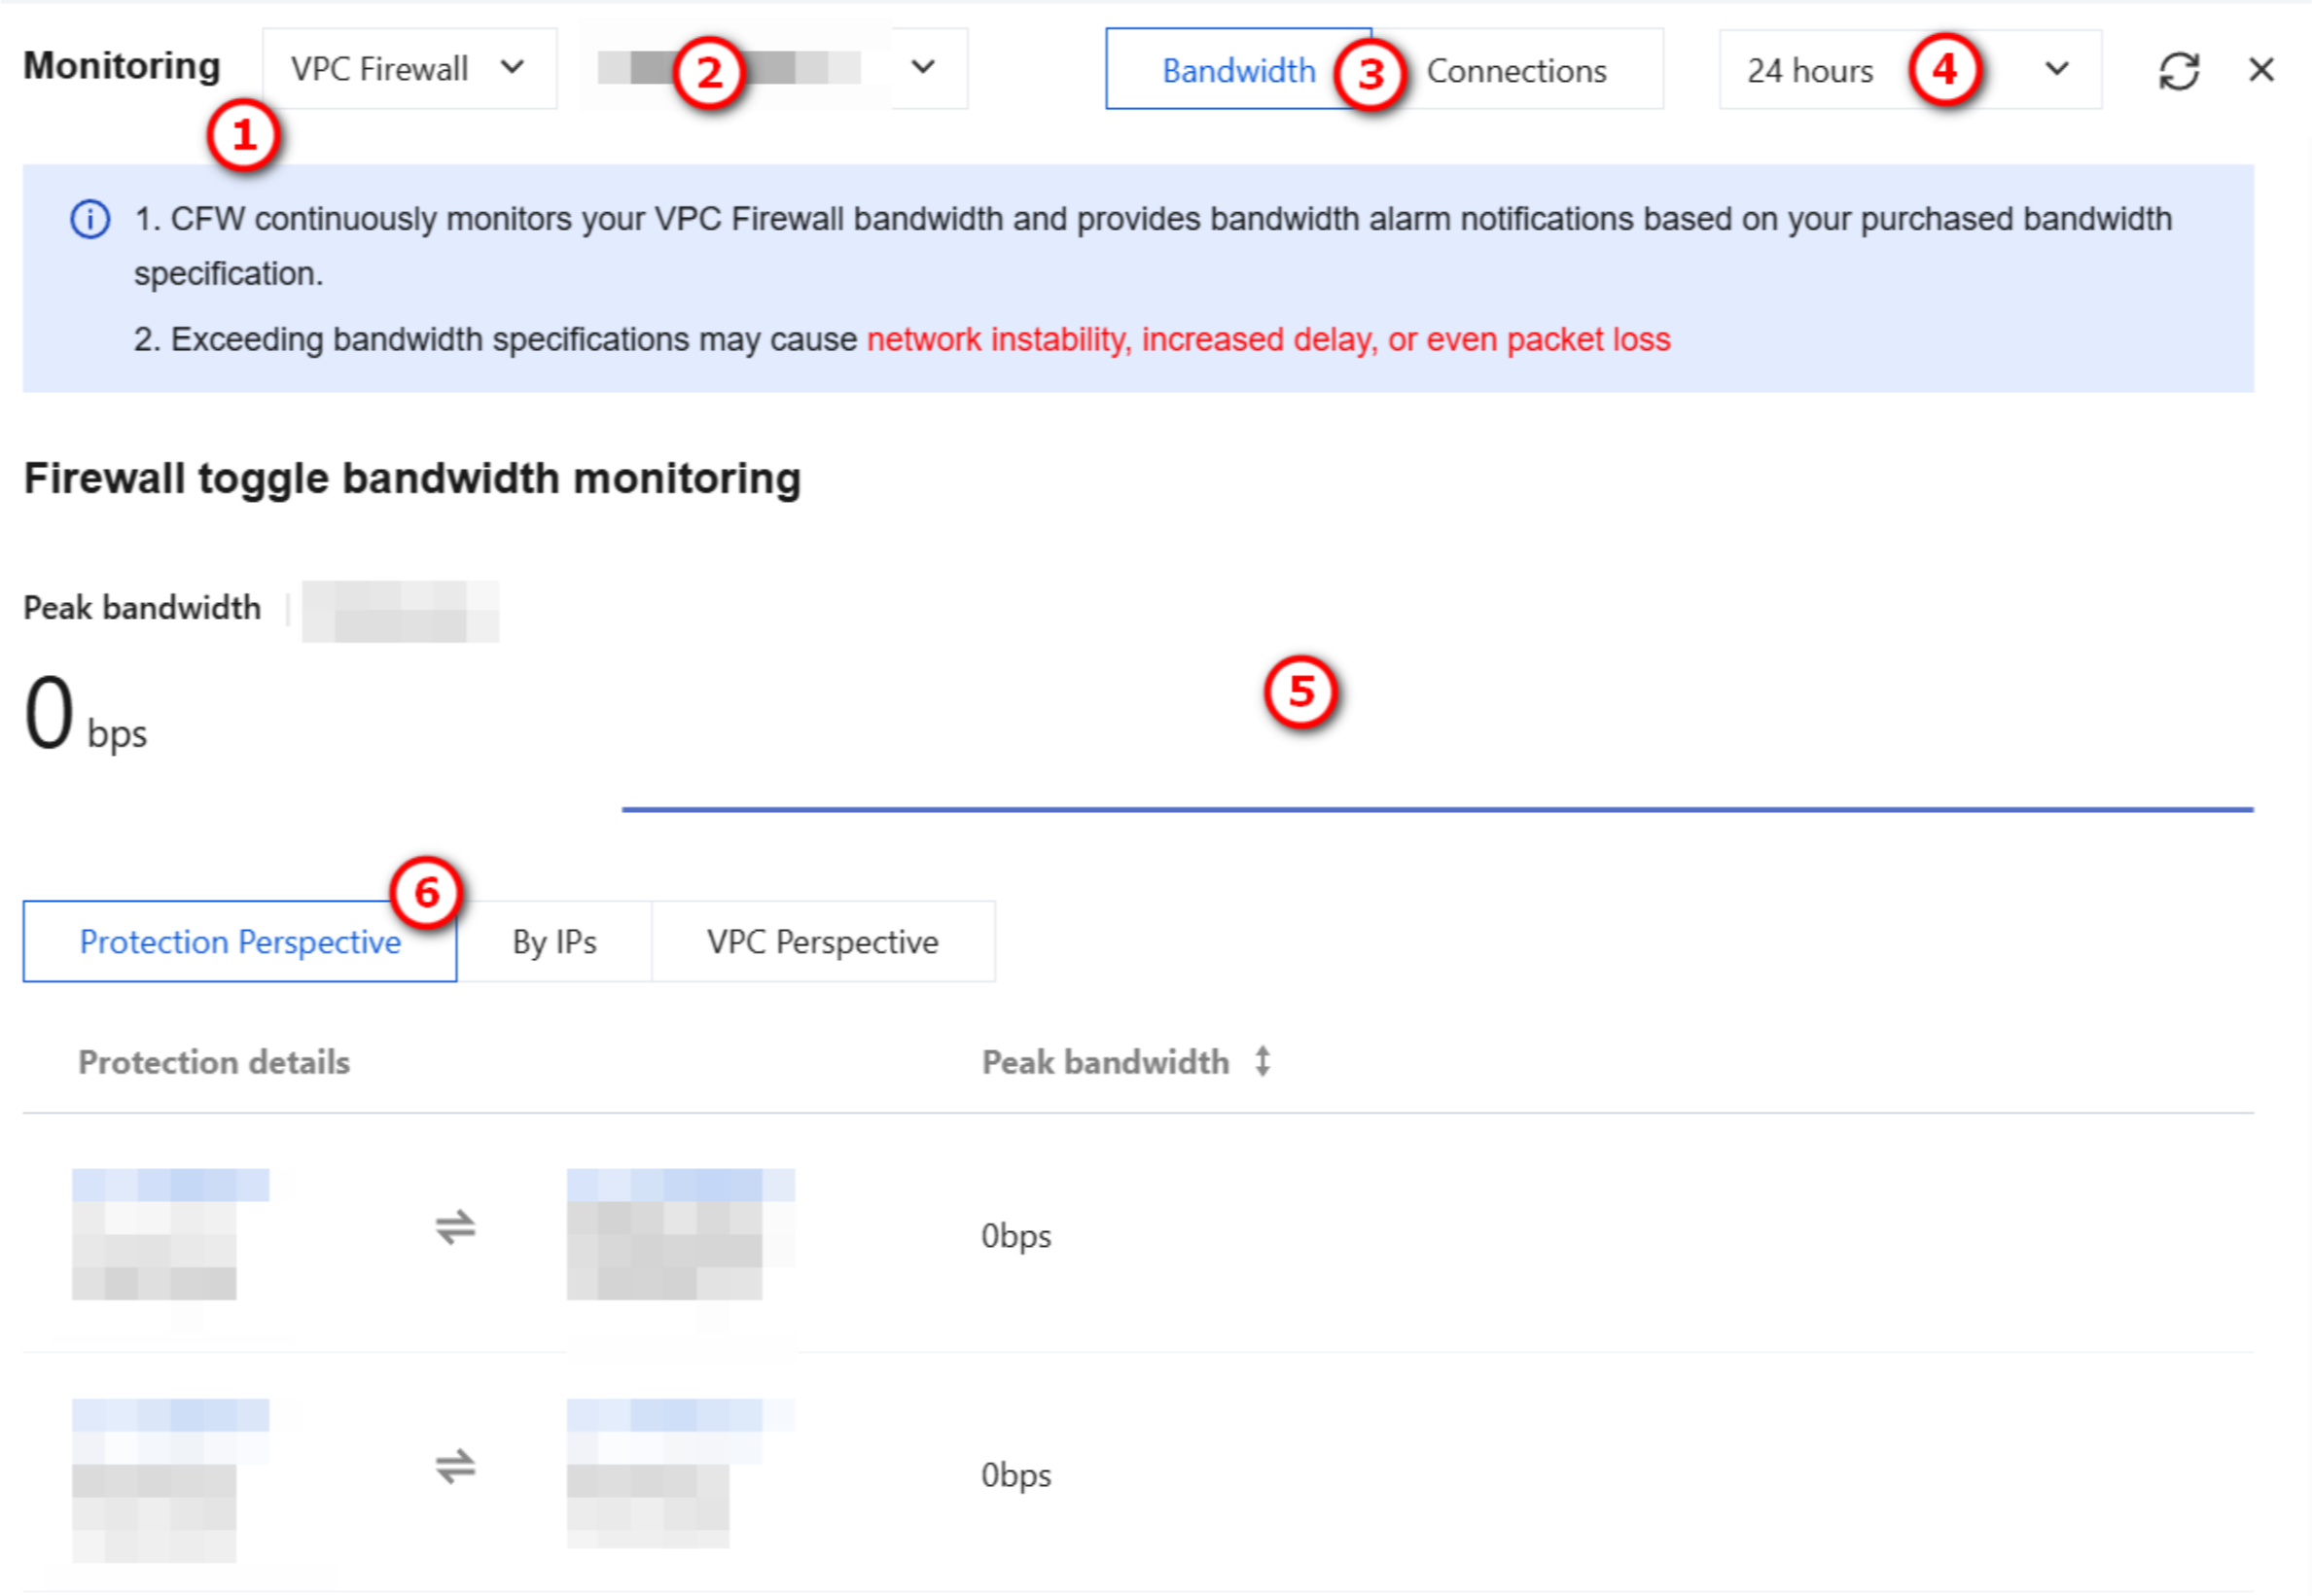
VPC Firewall status monitoring supports statistics on the bandwidth of each CCN instance.
1. In the upper-right corner of the bandwidth configuration panel, click View Monitoring.
2. On the Status Monitoring - VPC Firewall page, you can filter the bandwidth monitoring dimension based on CCN instance names, switch to view connection counts, and modify the statistical dimension by selecting a time range. You can also view monitoring curves and examine monitoring data from different perspectives.
Note:
Due to differences in statistical models and collection frequencies, there may be normal deviations between monitoring data and the Observability Platform.
Differences Between Primary/Secondary Mode and Cluster Mode
For differences between the primary/secondary mode and cluster mode editions of VPC Firewall, see the following table.